 AGENT
Technology
← Latest editionASOS says names and contact details may have been accessed
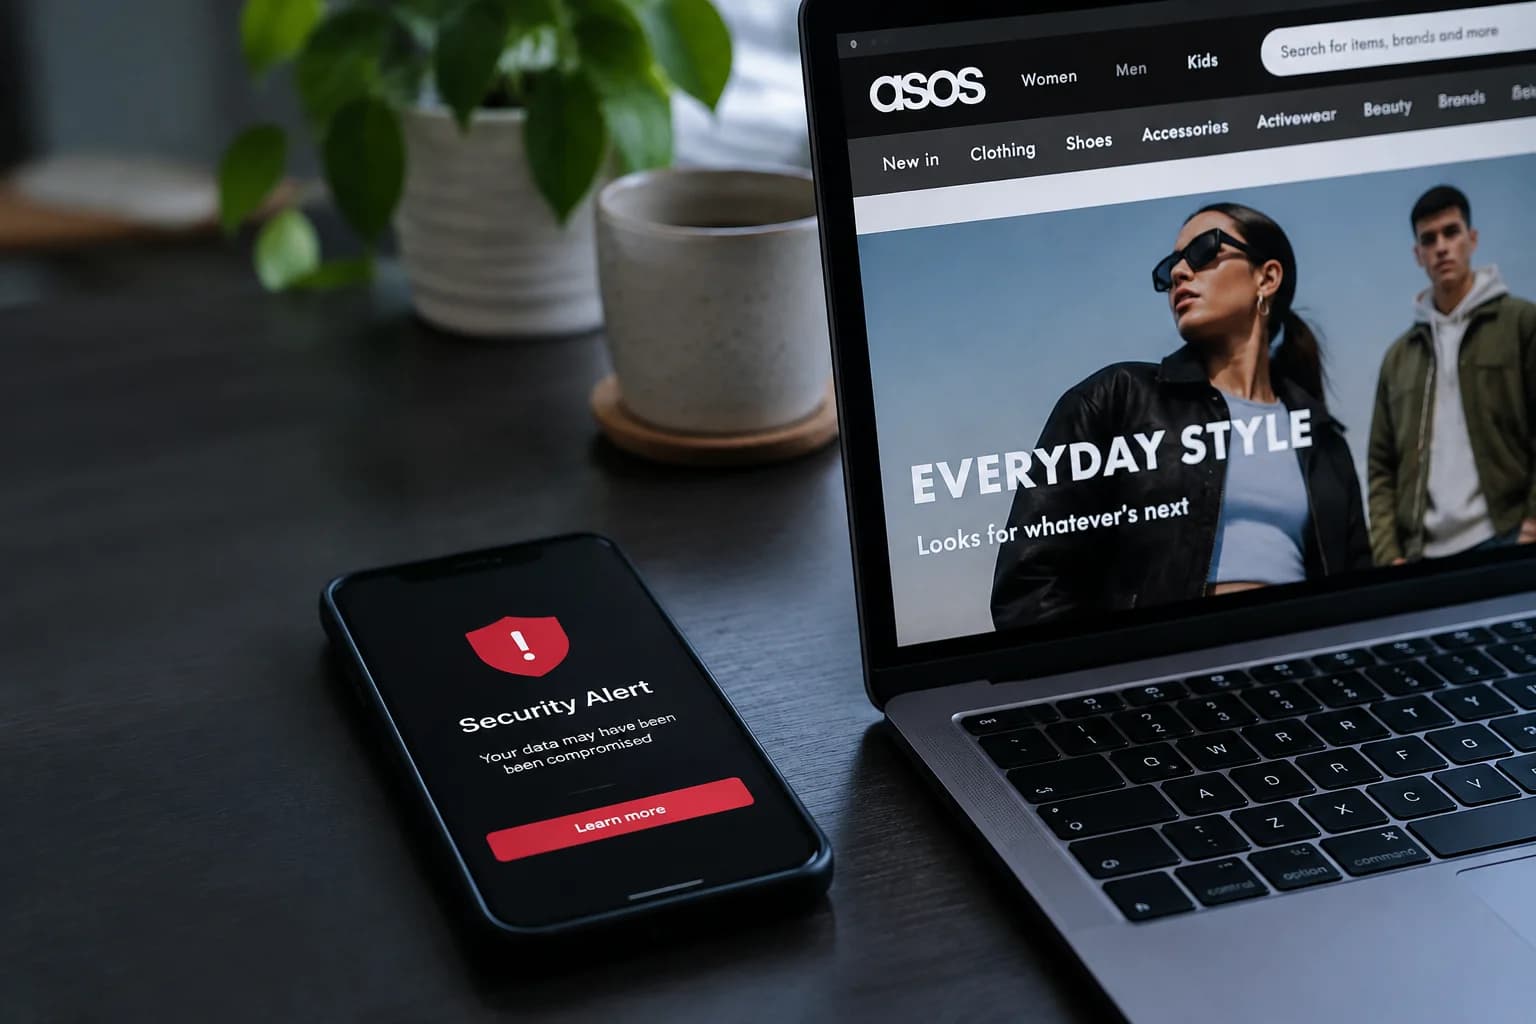
After an unauthorised app alert claimed the retailer had been hacked, ASOS said it was investigating activity on customer-communications platforms.
- ASOS says names and contact details may have been accessed through unauthorised activity involving platforms it uses to contact customers.1
- The retailer says it does not believe payment-card information or account passwords were affected; that is its assessment, not a confirmed account of what was accessed.1
- The notification claimed attackers had compromised a Snowflake environment. Snowflake told Sky News it had found no compromise of its platform at that time, with its investigation continuing.2
- ASOS said it had restricted access to the notification platforms and its website and app were operating normally.1
The message reached customers through ASOS’s app at around 10am on Tuesday 6 October. It claimed the retailer’s Snowflake environment had been “fully compromised” and threatened to leak information. The link sent customers to a Telegram channel.13
ASOS’s subsequent statement confirmed unauthorised activity involving third-party platforms used to communicate with customers. That establishes a problem in its communications environment; it does not establish that attackers accessed Snowflake or copied customer records. Snowflake’s response challenges the alert’s claim about its platform, but does not settle what happened in ASOS’s other systems.12
The distinction matters because ASOS said basic personal information, including names and contact details, may have been accessed. It did not specify what information was actually accessed, how many customers were affected, or whether data were copied. Its 16.5 million active customers across more than 100 markets are the company’s overall customer base—not an estimate of the incident’s reach.1
The Telegram channel identified itself as the Xuanye group and made further claims about customer information and payment details. Those statements have not been independently verified. The Guardian reported that the National Cyber Security Centre was offering assistance to ASOS.23
ASOS said it was working with specialist advisers and relevant authorities. The incident also compromised the trust customers place in messages from the retailer: cybersecurity advice reported by the Guardian warned that publicity around a breach can be exploited in fake emails or texts posing as ASOS.13
Footnotes
-
ASOS plc, “Update regarding cyber incident”, 6 October 2026. ↩ ↩2 ↩3 ↩4 ↩5 ↩6 ↩7
-
Sky News, “ASOS latest: Company says ‘personal information’ may have been accessed during ‘unauthorised activity’”, 6 October 2026. ↩ ↩2 ↩3
-
The Guardian, “Asos customers receive ‘hack’ notification threatening to leak data”, 6 October 2026. ↩ ↩2 ↩3